
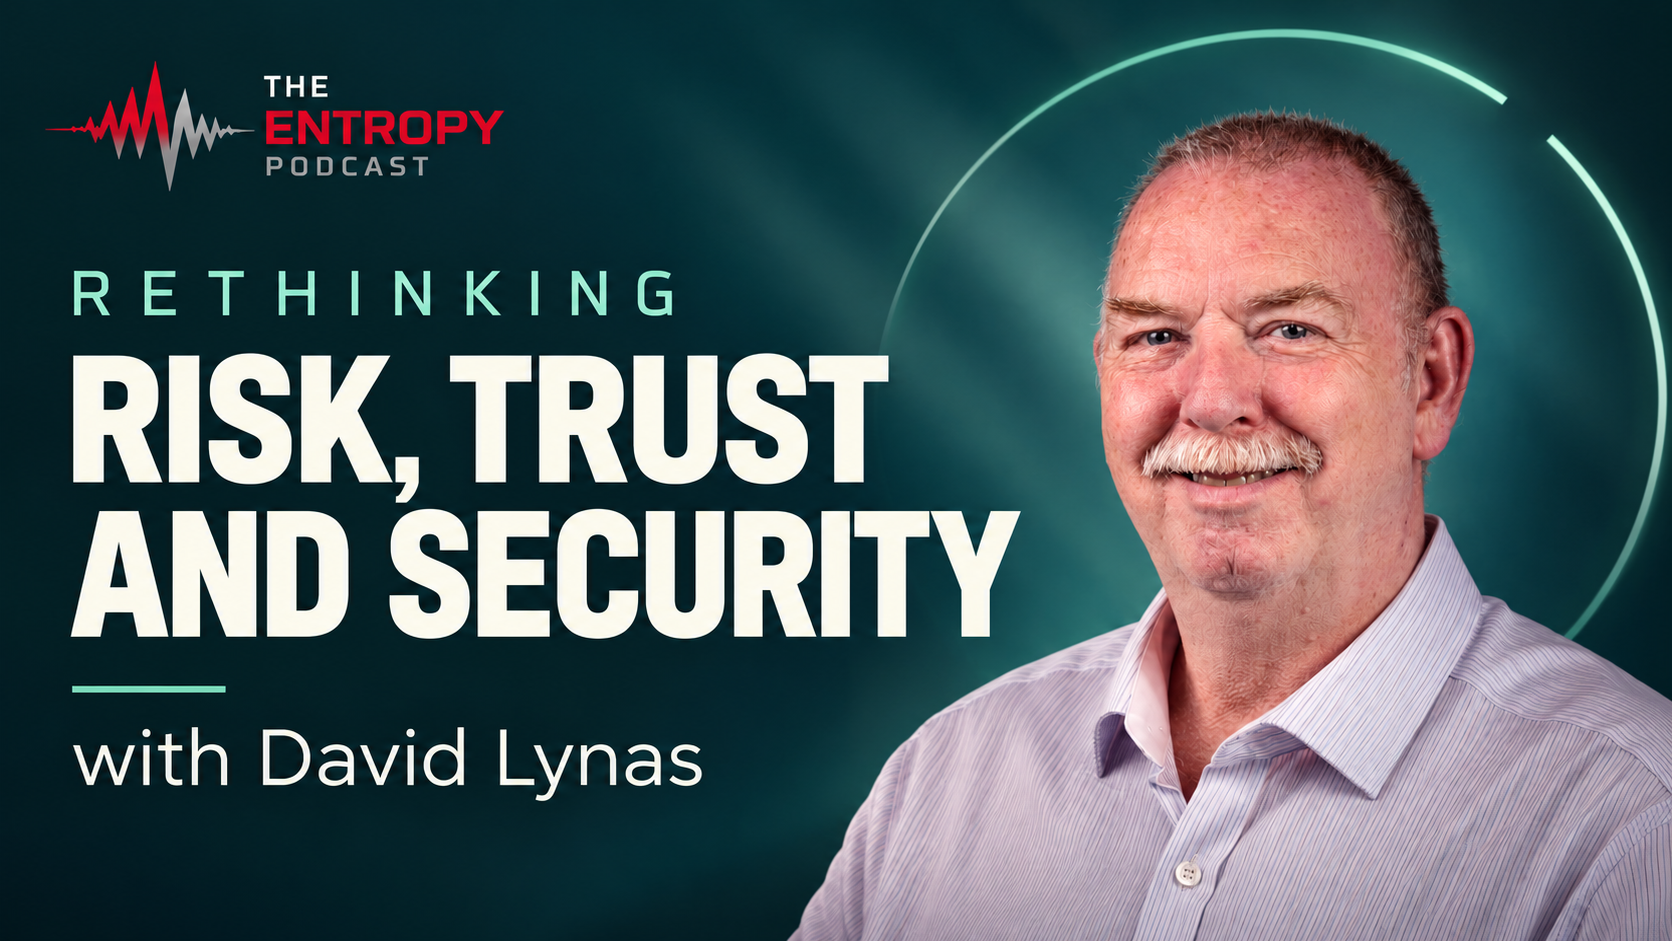
The Entropy Podcast – Rethinking Risk, Trust and Security
CEO David Lynas sat down with Francis Gorman for an Episode of the Entropy Podcast, released 1st November 2026.
What if the biggest problem in Security is how we explain its value?
Francis Gorman sits down with David Lynas, co-author of SABSA and founder of COSAC, for his first podcast interview. Drawing on 45 years in security, David challenges the idea that the security professionals job is simply to reduce risk and explains why helping businesses take the right risks matters just as much.
The episode explores the origins of SABSA, why risk assessments too often become paperwork exercises, and how to connect security decisions to outcomes business leaders actually care about. David also shares a striking banking example where the security architect’s recommendation was to remove controls.
From zero trust to AI moving faster than human oversight, this conversation asks what security must become to keep enabling innovation and why every security professional needs a clear answer to “so what?”
David Lynas Soundbites
- “The biggest risk is not understanding the nature of risk itself.”
- “We cannot possibly succeed without taking risk.”
- “We are not taking enough risk to reach our ambitions.”
- “The process is more important than the result, and that’s wrong.”
- “I didn’t go into business to achieve confidentiality.”
- “Trust should never mean I don’t know.”
- “What our profession does is extremely important and it’s getting more important every day.”
The Entropy Podcast Key takeaways
- Security should enable business success. Start with what the organisation wants to achieve, then show how security helps it get there.
- Risk management needs balance. A useful assessment should identify both insufficient protection and insufficient risk-taking to achieve business ambitions.
- Traceability makes security’s value visible. Connect each control to a defined requirement and a measurable outcome.
- Translate technical threats into business consequences. Leaders need to understand what lost availability means for customers, operations, and trust.
- Completing a process is not the same as making a good decision. Risk reports should inform action, rather than simply satisfy a reporting requirement.
- More security is not always better. Controls that obstruct the intended users can undermine the business purpose they are meant to support.
- Resilience deserves greater attention. Focus on maintaining essential outcomes when threats materialise and controls fail.
- Security must evolve alongside AI. David argues that rapid technological change demands adaptable approaches and clearer thinking about what must continue operating when things go wrong.
Podcast Links
Apple Podcasts: https://podcasts.apple.com/ie/podcast/rethinking-risk-trust-and-security-with-david-lynas/id1795927497?i=1000799067328